Services
Cybersecurity & resilience
Strengthen application, cloud, identity and operational security with assessment, engineering and incident readiness.
Prepare incident evidence before an incident
Response becomes more effective when ownership and records are already in place.
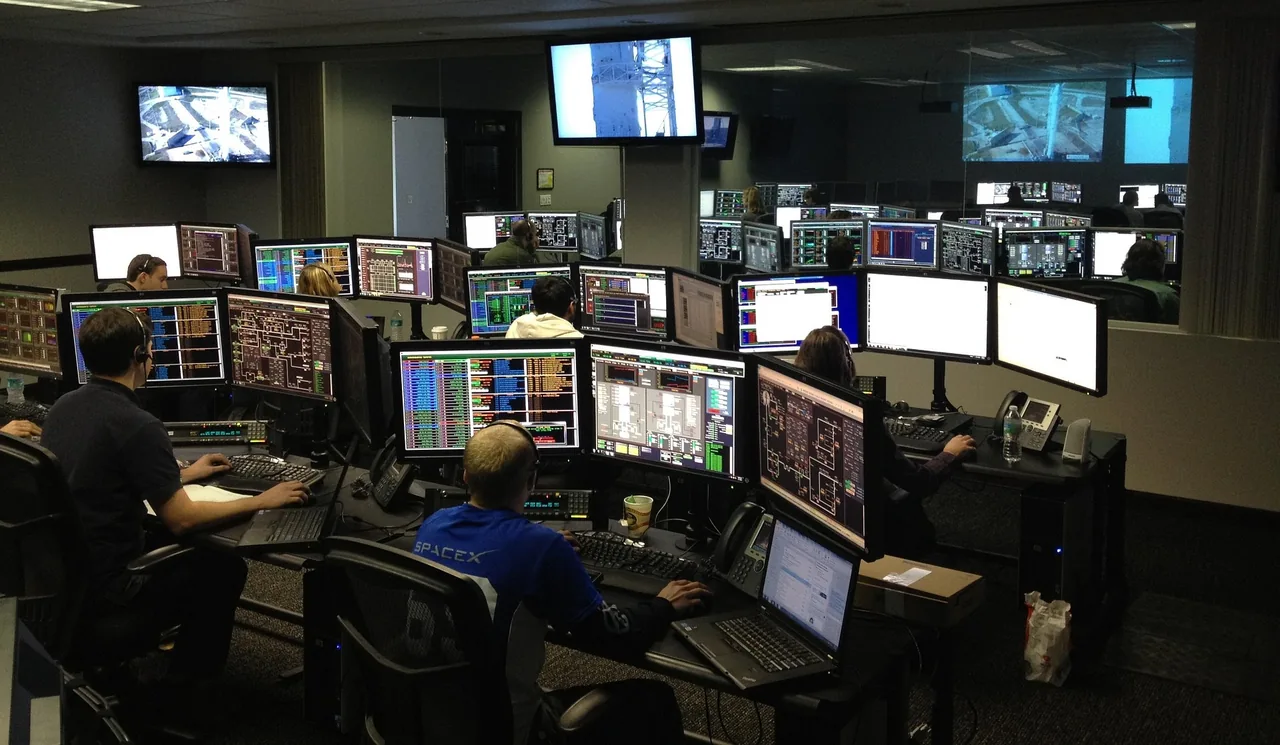
Map important systems, logs, timestamps and retention behavior. Confirm who can access the evidence and how it can be exported without losing context. A written incident plan cannot recover records that were never captured.
Identify the people who classify the incident, coordinate containment and evaluate applicable reporting duties. India’s CERT-In Directions and FAQs should inform the scoped process. Legal and security owners must interpret obligations for the actual organisation and incident.
Exercise an incomplete alert, an unavailable specialist and a dependency outside the organisation. Test evidence gathering and communication alongside technical recovery. Record what prevented the team from making the next decision.
Turn findings into assigned changes and retest the affected process. Recovery objectives and response expectations need evidence from exercises, not a generic promise. Keep the current runbook accessible to the people who will use it.
Map important systems, logs, timestamps and retention behavior. Confirm who can access the evidence and how it can be exported without losing context. A written incident plan cannot recover records that were never captured.